


Open Loop Workshop with Meta in Munich: Making AI and Data Rules Work in Practice
On 17 April 2026, we took part in a workshop hosted by Open Loop and the Datasphere Initiative in Munich. At the TUM Think Tank, we spent the afternoon exploring how rules for AI and data can enable innovation while providing reliable safeguards. The workshop was held under the Chatham House Rule, so we are sharing the format and topics rather than attributing individual remarks. This article covers what was discussed, how the EU regulatory landscape has evolved since then, and what businesses in South Tyrol and across the German-speaking region can take from it.
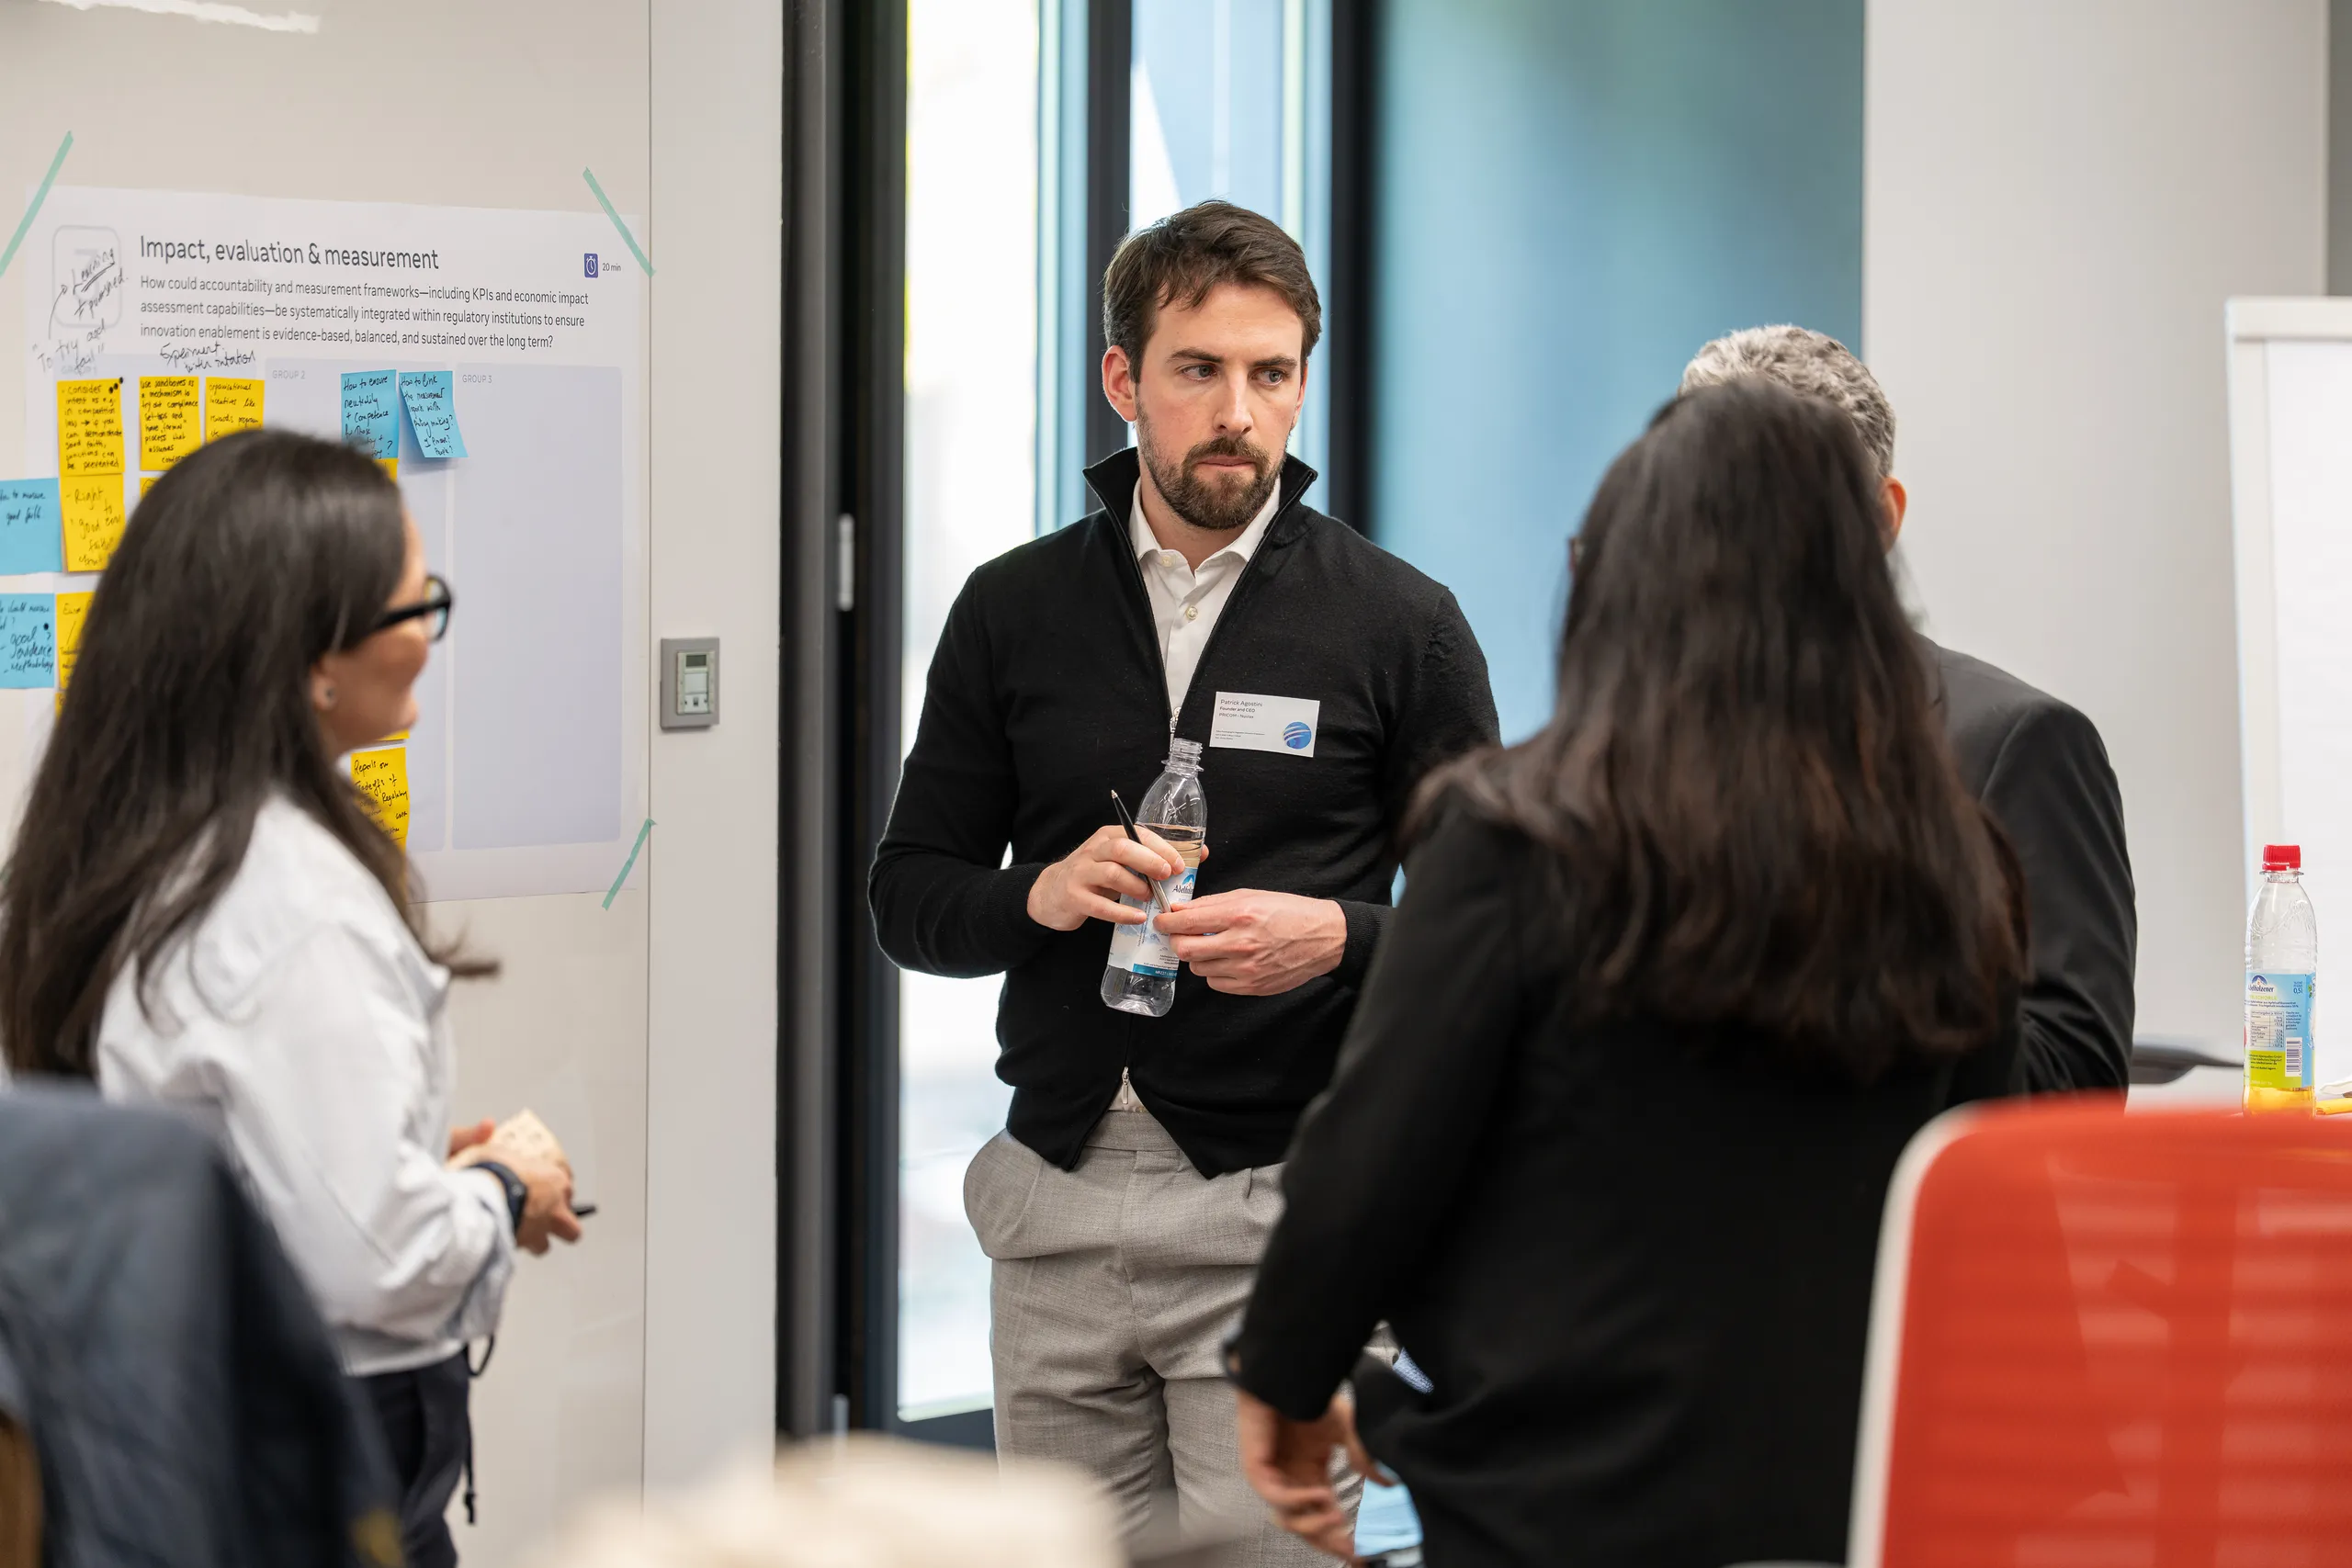
An Afternoon at the TUM Think Tank
Open Loop is a global Meta programme that brings policymakers and technology companies together to test rules for AI and other emerging technologies against real-world experience. Experts call this “policy prototyping”. The Datasphere Initiative, an international network focused on data governance, co-organised the event, which was hosted by the Technical University of Munich’s TUM Think Tank. We attended on behalf of Nuviax alongside PRICOM.
A small group of participants from academia, business, legal practice and industry associations in Germany, Italy, Switzerland and the UK had been invited. After lunch and a brief introduction, we moved into the working sessions. The afternoon ended with a plenary recap and a reception.
Working Together, Not Just Listening
Instead of presentations, there were three themed stations where small groups developed ideas and recommendations on physical workshop boards. The groups rotated between stations. The three topics were closely connected:
- Regulatory principles: the principles and foundations rules need to support innovation;
- Institutional design: how oversight, governance and regulatory tools should be structured;
- Regulatory practice and impact: how the application, effects and effectiveness of rules can be measured.
A common misconception is that the Chatham House Rule prevents anyone from reporting on an event. It does not. Participants may share the information discussed, but must not identify the speakers or their organisations. That is the approach we take here.
EU Reform: Where Things Stand in November 2026
The agenda looked ahead in the context of ongoing EU reform, including the omnibus packages, the Digital Fitness Check and implementation of the AI Act. A great deal has happened since April. Here is where things stand:
- AI Omnibus: Regulation (EU) 2026/1744 was published on 24 July 2026 and entered into force on 27 July 2026. It postpones obligations for high-risk AI until 2 December 2027 for standalone systems and 2 August 2028 for AI in regulated products. The structure and risk-based approach of the AI Act remain in place.
- Data Omnibus: This covers, among other things, the GDPR, ePrivacy, the Data Act and reporting obligations for cyber and data incidents. The Commission proposed it on 19 November 2025, and the Council adopted its negotiating mandate on 21 October 2026. Parliament has yet to adopt a position; trilogue negotiations can begin only after that. The Council wants to retain the definition of personal data and use a new Article 25a to clarify when pseudonymised data counts as personal data.
- Digital Fitness Check: The consultation ran from 19 November 2025 to 11 March 2026. Results and any further proposed changes are expected in 2027.
Until changes are agreed, the current legal provisions apply. For businesses in Italy, obligations under Legislative Decree 138/2024 and the GDPR remain unchanged.
What We Took Away from Munich
What follows is our own assessment, not an account of individual contributions to the discussion. First, simplification does not mean obligations disappear. Core principles, such as the security of processing under Article 32 of the GDPR, remain the benchmark for regulators and customers. Second, the postponement for high-risk AI creates time to prepare, not a free pass. Businesses that use it to get organised will save work later.
Third, and this connects the three workshop themes, the impact of a rule depends on how it is applied, reviewed and measured. For businesses, demonstrable day-to-day practice matters more than a document kept on file for a potential crisis.
What Business Leaders Should Do Now
- Take stock of AI use: create an inventory of every AI system in use, including tools with built-in AI, and record its purpose, the types of data it processes and its provider.
- Clarify your role: document whether your company develops AI, offers it under its own name or simply uses it in its operations. Your obligations depend on that distinction.
- Secure access: limit permissions in systems that hold personal data, enable multi-factor authentication and turn on logging.
- Review contracts: put an Article 28 GDPR data processing agreement in place with every AI service provider that processes personal data on your behalf.
- Assign responsibility: appoint someone to monitor legislation and deadlines, and add 2 December 2027 and 2 August 2028 to your planning calendar.
- Document decisions: briefly document why an AI tool is being used and which risks have been assessed.
At Nuviax, we provide practical, step-by-step support through our AI compliance services, working alongside our data protection expertise and tailored to how AI is actually used.
Conclusion
The workshop in Munich showed that rules for AI and data can be developed together with the people who will apply them. That is good news for businesses: if you know your systems, define responsibilities and keep clear records, you will be prepared for whichever version of the rules takes effect. Starting early and taking a structured approach keeps the workload manageable.
Getting your operations in order is the best response to any regulatory reform.
Verwandte Artikel
Data Protection and Information Security in Hotels: What Hospitality Businesses Need to Consider Now
Hardly any industry processes so much sensitive data in such a confined environment as the hotel industry. From the booking and the ID presented at check-in to payment and breakfast preferences: Within just a few minutes, a hospitality business collects information that would require entire series of forms in other companies. The fact that this also gives rise to obligations can quickly fade into the background of day-to-day operations. This involves two interconnected areas: data protection - the legally compliant handling of personal data - and information security, the technical and organisational protection of that very data. This article explains what data hotels collect, which legal obligations apply in Italy and where the most common vulnerabilities lie.
How to label AI content correctly: A practical guide for websites and social media
Since 2 August 2026, the transparency obligations under Article 50 of the EU AI Act have applied. Anyone using chatbots, AI images, AI voices or AI-generated text has since been asking: Do I now have to label all of it? The short answer is no. The AI Act does not require companies to label every piece of AI-generated content—the obligations apply to clearly defined situations, not every use of an AI tool. This is precisely where the practical problem arises: some companies label everything out of uncertainty and therefore appear unprofessional. Others label too little and risk a violation. This article explains the four cases governed by Article 50, the applicable exceptions and exactly how to label content on websites and social media.
NIS2 from 2026: These obligations are coming for SMEs.
The NIS2 Directive (EU 2022/2555) is the European Union's most far-reaching cybersecurity regulation to date - and it affects significantly more companies than its predecessor. Many SMEs still assume that ‘cybersecurity obligations’ apply only to large corporations or critical infrastructure. That misconception can be costly. As transposition into national law is taking effect gradually in several Member States, 2026 will be the year of practical application for many companies. Those who do not start now will come under time pressure. This article summarises who is affected, which obligations apply and where management bears personal responsibility.


